Michael J. Bannach: Where Does Controlled Data Go When an Engineer Uses AI?
Congress has told the Pentagon to fold AI security into DFARS and CMMC. For defense suppliers, the more urgent question is where their people are pasting controlled data today.
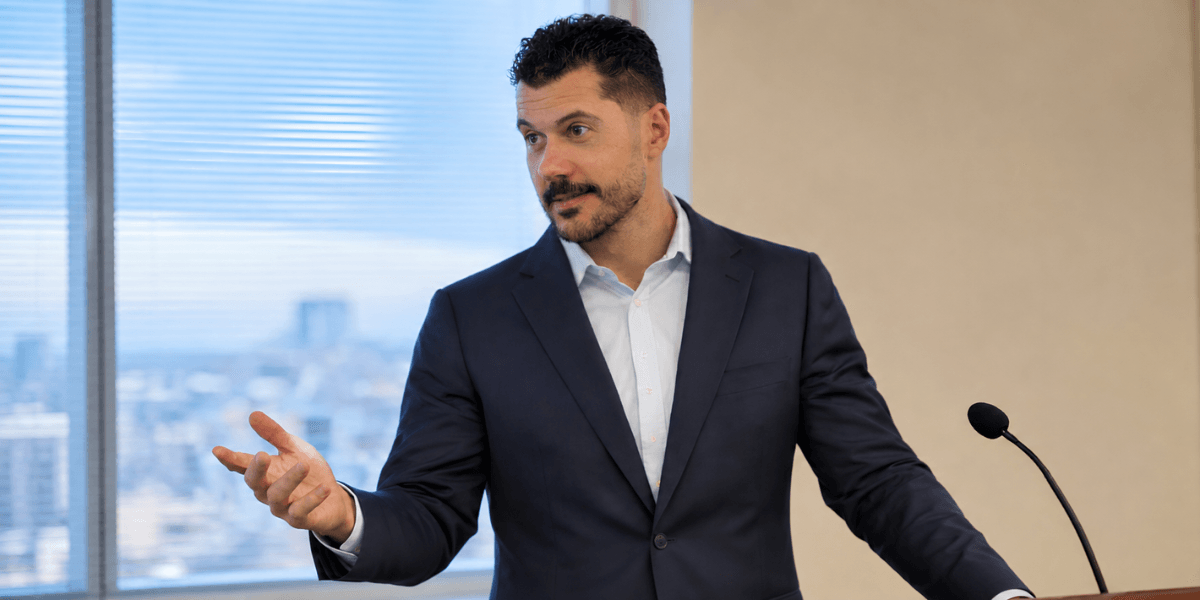
Ask a defense supplier where its controlled unclassified information lives, and most can point to a file server, a cloud tenant or an enclave. Ask where that information goes when an engineer wants help summarizing a specification, and the answers get vague. Michael J. Bannach, President and CEO of Stealth Technology Group (STG), believes that gap is where the next wave of compliance findings will come from.
“Every assessment starts with the same question: where does the data go?” said Bannach, a CISSP whose firm is a Cyber AB Registered Practitioner Organization. “AI tools answer that question in ways most companies haven’t mapped. A meeting assistant that records a call, a browser extension that reads a page, a chatbot someone pastes a drawing note into. Each one is a new path out of the boundary.”
The Law Is Already Moving
Section 1513 of the National Defense Authorization Act for Fiscal Year 2026, signed December 18, 2025, directs the Pentagon to develop a security framework for the artificial intelligence and machine learning systems it acquires, including model weights, as an extension of its existing cybersecurity frameworks, and to carry those requirements into the DFARS and CMMC. A status update to Congress was due in June 2026.
The framework has not been published, and the Pentagon suspended CMMC Phase II on July 13, 2026, while the Department reviews the program. Bannach cautions suppliers against reading the pause as a reprieve on AI. The rules that govern controlled data today already apply to every tool that touches it. Under DFARS 252.204-7012, a contractor that uses an external cloud service to store, process or transmit covered defense information must ensure the provider meets security requirements equivalent to the FedRAMP Moderate baseline. Consumer AI services were not built with that requirement in mind.
What Employees Are Already Doing
The usage is real. Verizon’s 2025 Data Breach Investigations Report found that 15 percent of employees routinely accessed generative AI on corporate devices, and that 72 percent of them signed in with non-corporate email accounts, outside the company’s identity controls. By the 2026 report, frequent AI use had reached 45 percent of employees. IBM’s 2025 Cost of a Data Breach Report found that 97 percent of organizations that reported a breach of an AI model or application lacked proper AI access controls.
“Nobody pastes controlled technical data into a chatbot to be malicious,” Bannach said. “They do it because they’re on deadline. The fix isn’t a memo. It’s giving people an approved tool inside the boundary and making the unapproved path harder than the approved one.”
A Practical Plan for the Pause
Section 1513 targets AI the Pentagon acquires and the contractors that develop, deploy, store or host it. Bannach recommends that every supplier use the pause to bring AI under the controls that already apply, rather than wait for a rule.
The first step is an inventory of every AI capability that touches the environment where controlled information lives, including features built into tools the company already owns: meeting transcription, email assistants, document summarization and code completion. Many of these arrive through routine software updates, switched on by default.
The second step is a boundary decision for each tool. Either it is approved for controlled information, running inside the assessed boundary or on a cloud service that meets the FedRAMP Moderate equivalency requirement, or it is blocked from controlled information entirely. Location alone does not settle the question; each approved use still needs documented controls behind it. A “non-sensitive use only” label is not enough unless the company can enforce the separation and demonstrate it.
The third step is documentation. The System Security Plan should describe which AI tools are in use, what data they may touch and how that limit is enforced. “An assessor is going to ask,” Bannach said. “The best time to write that answer is before the question.”
The fourth step is policy and training that tell engineers what to use, not only what to avoid. A block without an alternative sends people to their personal phones.
Because Congress told the Pentagon to build on existing frameworks rather than start over, the controls suppliers already maintain for NIST SP 800-171 are the natural foundation. The NIST AI Risk Management Framework offers a common vocabulary for the AI-specific pieces. STG applies the same boundary-first thinking in its AI strategy and governance work with regulated companies.
Ready for Both
The suppliers that treat the pause as time to build, rather than time off, will be ready for two things at once: the CMMC requirements when they return, and whatever AI requirements follow from Section 1513.
“The suppliers who handle this well will treat AI like any other system in the boundary: inventoried, scoped, documented and monitored,” Bannach said. “When AI requirements reach the DFARS, they’ll be starting from a documented baseline instead of a blank page.”
STG helps defense suppliers scope their controlled-information environments, AI tools included, through a CMMC readiness assessment.
Michael J. Bannach is President and CEO of Stealth Technology Group (STG), one accountable partner for IT, cybersecurity, compliance and AI for regulated mid-market companies and defense suppliers. STG is a Cyber AB Registered Practitioner Organization with teams serving Tampa, Sarasota, Boston and Greater Philadelphia. A CISSP with more than 25 years in enterprise IT and cybersecurity, Bannach also holds CCNP Enterprise and CCNP Collaboration certifications, a certificate in AI products and services from MIT, and an Executive MBA from Saint Joseph’s University. Learn more at michaelbannach.com.

Today US Contributor
Hailey Anderson
Covers business, digital culture, and entrepreneurship, exploring how new ideas and technologies are changing industries.
This article features partner, contributor, or branded content from a third party. Members of the Today US editorial staff were not involved in the creation of this content. All views and opinions are those of the contributor alone.
You may also like
How Phaedra Solutions Helps Businesses Build and Launch AI Products
Vision Ranking Turns Google Visibility Into Growth
Every Box Was Green. The Deal Was Dead.
Atlantic Health Strategies: Building Quality and Lasting Success in Behavioral Health
Evolve Leadership And Development Leads From Within